Is Your Organization Ready for NIS2 Compliance?
Identify compliance gaps, strengthen cyber resilience, and accelerate your NIS2 readiness with proven cybersecurity solutions, managed services, expert guidance, and employee awareness programs.
Get a Free NIS2 Readiness Review
Our cybersecurity experts will help you understand your current compliance status, identify gaps, and recommend the right technologies and services to support your NIS2 journey.
🔍 Gap Analysis
Review your current security controls against NIS2 requirements.
🛡 Security Assessment
Understand your biggest risks and recommended improvements.
📋 Compliance Roadmap
Receive practical recommendations and next steps toward compliance.
30-minute expert consultation • No obligation •
Broadened Scope of the NIS2 Directive
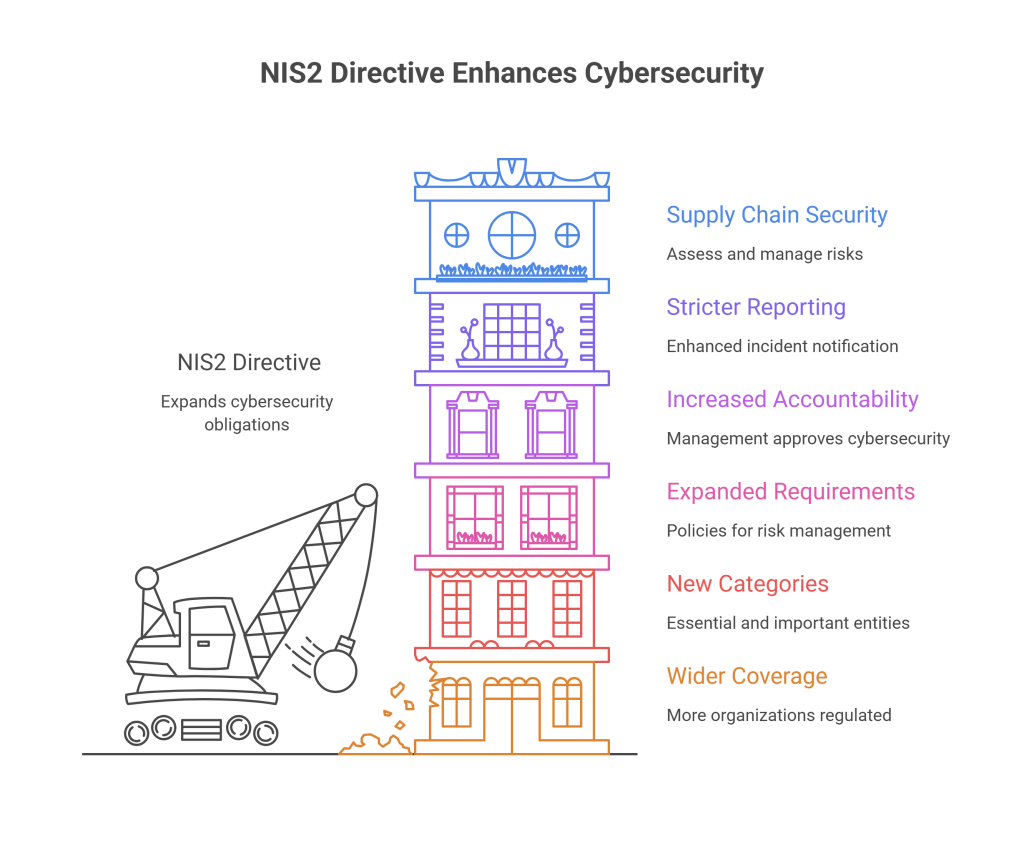
Compared to NIS1, the NIS2 Directive significantly expands the scope of organizations subject to cybersecurity and reporting obligations. The new framework introduces a wider sector coverage, stronger governance requirements, increased management accountability, and stricter cybersecurity risk-management measures.
🏢 More Organizations Covered
NIS2 extends cybersecurity obligations to a significantly larger number of medium and large organizations operating in sectors of high criticality and other critical sectors, increasing the number of regulated entities across the European Union.
⚡ Essential & Important Entities
NIS2 replaces many of the previous NIS1 classifications with the new categories of Essential Entities and Important Entities, creating a more consistent supervisory framework across Member States.
🔒 Expanded Cybersecurity Requirements
Organizations must implement policies covering risk management, incident handling, business continuity, disaster recovery, supply chain security, vulnerability management, encryption, access control and multi-factor authentication.
👔 Increased Management Accountability
Management bodies are required to approve, oversee and receive training on cybersecurity risk-management measures. Senior leadership is expected to actively participate in cybersecurity governance.
🚨 Stricter Incident Reporting
NIS2 introduces enhanced incident reporting obligations and tighter notification timelines, requiring organizations to establish mature detection, response and reporting processes.
🔗 Supply Chain Security
For the first time, organizations must formally assess and manage cybersecurity risks arising from suppliers, service providers and third-party relationships throughout the supply chain.
Examples of Sectors Covered by NIS2
Energy • Transport • Banking • Financial Market Infrastructures • Healthcare • Drinking Water • Wastewater • Digital Infrastructure • ICT Service Management • Public Administration • Space • Manufacturing • Postal and Courier Services • Waste Management • Food Production • Digital Providers • Research Organizations
Roadmap: From NIS1 to NIS2
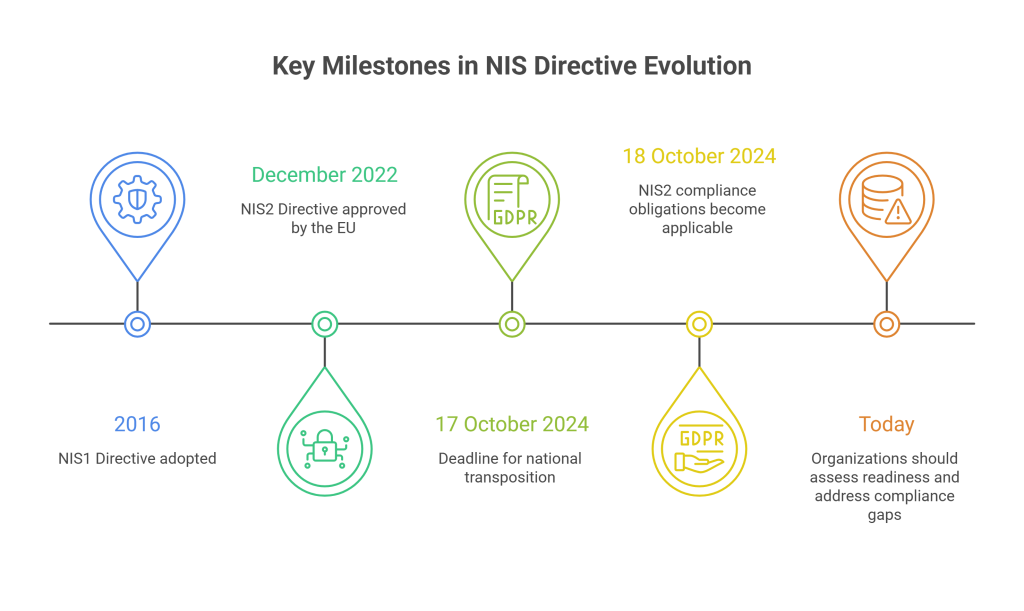
The European Union began its cybersecurity regulatory journey in 2016 with the adoption of the first Network and Information Security Directive (NIS1 Directive), establishing a common framework for improving cybersecurity across Member States.
Recognizing the rapidly evolving cyber threat landscape, the European Parliament and the Council of the European Union adopted the NIS2 Directive in December 2022. NIS2 significantly expands the scope of cybersecurity obligations, introduces stronger governance requirements, and applies to a broader range of essential and important entities across critical sectors.
As a directive, NIS2 must be transposed into national legislation by each EU Member State. The deadline established by the European legislator for national implementation was 17 October 2024, with compliance obligations becoming applicable from 18 October 2024.
Organizations should not wait for enforcement actions to begin. Early preparation enables management teams to identify compliance gaps, strengthen cybersecurity resilience, reduce operational risk, and establish a clear roadmap toward NIS2 readiness.
Key Milestones
- 2016 – NIS1 Directive adopted
- December 2022 – NIS2 Directive approved by the EU
- 17 October 2024 – Deadline for national transposition
- 18 October 2024 – NIS2 compliance obligations become applicable
- Today – Organizations should assess readiness and address compliance gaps
🔐 NIS2 Cybersecurity Compliance Solutions
Comprehensive cybersecurity products and services designed to help Essential and Important Entities meet NIS2 Directive requirements and achieve regulatory compliance.
Member States shall ensure that members of the management bodies of essential and important entities receive appropriate cybersecurity training. Organizations should also provide regular cybersecurity awareness training to employees to improve their ability to identify risks, assess cybersecurity practices and understand their impact on business operations and critical services.
| 🎓 Sophos Training & Certifications Vendor Sophos - Training and Certifications |
Provides professional cybersecurity training courses and certification programs that help organizations, IT teams and security professionals develop the knowledge and skills required to manage and maintain modern cybersecurity environments effectively. |
| 🎣 Sophos Phish Threat Vendor Sophos - Phish Threat |
Delivers simulated phishing campaigns and security awareness training to help employees recognize phishing attacks, social engineering attempts and other cyber threats. Training content covers phishing awareness, password protection, data loss prevention and general cybersecurity best practices. |
| 🎓 CISOedu Cybersecurity E-Learning Platform Vendor AdvisionIT - Security Awareness Training |
Provides structured cybersecurity awareness training that educates employees and management teams on how to recognize cyber threats, protect sensitive information, comply with regulatory requirements and improve the organization's overall cybersecurity posture. |
| 📚 Managed Security Awareness Training Vendor AdvisionIT - Managed Security Awareness Training |
Delivers ongoing managed cybersecurity awareness programs designed to address the human factor in cybersecurity, support compliance initiatives, strengthen security culture and help organizations meet NIS2 governance and training requirements. |
Member States shall ensure that essential and important entities take appropriate and proportionate technical, operational, and organisational measures to manage risks posed to the security of network and information systems based on policies for risk analysis and information system security.
| 🛡 Sophos Intercept X for Workstations & Laptops Intercept X for Servers |
Integrates deep learning AI, anti-exploit, anti-ransomware, and threat intelligence technologies to prevent, detect, investigate, and remediate attacks across endpoints and servers. |
| 🔥 Sophos Firewall Firewall SECaaS Firewall Brochure Network Switches |
Provides next-generation firewall protection, ransomware prevention, web filtering, URL filtering, application control, malware detection, cloud filtering, and network segmentation capabilities. |
| ☁ Sophos Cloud Optix Cloud Security Posture Management |
Continuously monitors cloud infrastructure configurations, detects misconfigurations, and automatically helps remediate cloud security risks across AWS, Azure, and Google Cloud. |
| 🔄 Sophos Synchronized Security | Enables coordinated communication between firewalls, endpoints, servers, and cloud environments to accelerate detection, isolation, and remediation of advanced threats. |
| 🚨 Sophos MDR Managed Detection & Response |
Provides 24/7 managed threat hunting, monitoring, investigation, response, and remediation services to identify attacks that traditional tools may miss. |
| 📊 Logsign Unified SecOps SIEM • SOAR • XDR |
Delivers centralized visibility, security analytics, orchestration, automation, incident response workflows, and compliance reporting from a unified cybersecurity operations platform. |
Member States shall ensure that essential and important entities implement appropriate incident handling measures, including detection, response, recovery, investigation and reporting of cybersecurity incidents.
| 🚨 Sophos MDR Vendor Sophos - Managed Detection and Response (MDR) for Servers SECaaS Price Vendor Sophos - Managed Detection and Response for Workstations/Laptops SECaaS Price Vendor Sophos - Managed Detection and Response (MDR) Datasheet |
Continuously monitors signals from across the security environment, including network, email, firewall, identity, endpoint and cloud technologies. Provides 24/7 incident response coverage delivered by IR experts, including threat investigation, root cause analysis, remediation and reporting. |
| ⚡ Sophos Rapid Response Vendor Sophos - Rapid Response Service |
Enables immediate expert-led response to active security incidents by identifying, investigating and neutralizing threats before they can cause significant business impact. |
| 🔄 Sophos Synchronized Security | Shares telemetry and security health status across firewalls, endpoints and servers, enabling coordinated detection, isolation and malware remediation during security incidents. |
| 🛡 Acronis XDR Vendor Acronis - XDR Solution |
Provides Advanced Security and XDR capabilities that improve visibility, investigation and response across endpoints, identities, cloud environments and workloads. |
| 🛡 Acronis MDR Vendor Acronis - MDR Solution |
Managed Detection and Response service delivering proactive monitoring, investigation, threat hunting and expert response capabilities. |
| 🎯 CrowdStrike Falcon Complete MDR Vendor CrowdStrike - XDR & MDR Solution Falcon Complete Next Generation MDR |
Provides fully managed detection and response services with expert threat hunting, investigation, containment, remediation and continuous threat monitoring. |
| 🛡 Bitdefender MDR Plus Vendor Bitdefender - XDR & MDR Solution |
Combines XDR analytics, threat intelligence, continuous monitoring and managed incident response services to strengthen incident handling and cyber resilience. |
Member States shall ensure that essential and important entities implement appropriate business continuity measures, including backup management, disaster recovery capabilities and crisis management procedures to ensure resilience and recovery from cybersecurity incidents.
| 🚨 Sophos MDR Vendor Sophos - Managed Detection and Response (MDR) |
Ensures the information security aspect of business continuity management through 24/7 detection and response to cyber threats across the IT environment, leveraging human expertise, artificial intelligence and advanced security technologies. |
| 🛡 Sophos Intercept X Vendor Sophos - Intercept X Vendor Sophos - Intercept X for Server |
Integrates deep learning AI, anti-exploit and anti-ransomware protection to prevent, detect and remediate attacks. Includes ransomware rollback capabilities, restoration of original files and forensic-level remediation to support operational resilience and business continuity. |
| ☁ Sophos Cloud Optix Vendor Sophos - Cloud Optix SECaaS |
Monitors AWS, Microsoft Azure and Google Cloud environments for storage services without backup schedules enabled and provides visibility and guided remediation to reduce business continuity risks. |
| 💾 Acronis Cyber Protect Cloud Vendor Acronis - Backup & Disaster Recovery Cloud Solutions |
Acronis Cyber Protect Cloud combines backup, disaster recovery, next-generation anti-malware protection and endpoint management in a single platform. This integrated cyber protection approach simplifies recovery processes, improves operational resilience and helps organizations recover quickly from cyber incidents. |
Member States shall ensure that essential and important entities implement appropriate supply chain security measures, including security-related aspects concerning relationships with direct suppliers, third-party vendors and service providers.
| 🛡 Sophos Intercept X with XDR Vendor Sophos - Intercept X with XDR for Laptops Vendor Sophos - Intercept X with XDR for Servers |
Provides comprehensive defense-in-depth protection against threats introduced through third-party suppliers and service providers. Combines AI-powered protection, exploit prevention, behavioral analysis, anti-ransomware capabilities and advanced XDR functionality to identify, investigate and respond to suspicious activities across endpoints and servers. |
| 🚨 Sophos Managed Detection & Response (MDR) Vendor Sophos - Managed Detection and Response (MDR) for Laptops & Workstations Vendor Sophos - Managed Detection and Response (MDR) for Servers |
Delivers expert threat hunting, continuous monitoring and incident remediation as a fully managed service. Sophos security specialists proactively hunt for, validate and respond to potential supply chain threats, malicious activity and third-party compromise attempts around the clock. |
| 🔐 Sophos Zero Trust Network Access (ZTNA) Vendor Sophos - ZTNA |
Protects against supply chain attacks by enforcing granular access controls for suppliers, contractors and trusted partners. Continuously validates user identity, device health and compliance before granting access to business applications and resources, regardless of user location. |
Member States shall ensure that essential and important entities implement appropriate measures for the secure acquisition, development and maintenance of network and information systems, including vulnerability management, vulnerability disclosure and remediation processes.
| 🚨 Sophos Managed Detection & Response (MDR) Vendor Sophos - Managed Detection and Response (MDR) |
Threat-hunting experts continuously monitor and investigate alerts across network, firewall, cloud, email and endpoint infrastructure. Sophos MDR proactively supports vulnerability disclosure investigations, identifies potential exploitation attempts, performs remediation activities and provides detailed human-authored analysis and reporting. |
| 🔍 Acronis Vulnerability Assessment & Patch Management Vendor Acronis - Vulnerability Assessment and Patch Management |
Provides automated vulnerability assessment and patch management capabilities that help identify, prioritize and remediate security vulnerabilities across supported Microsoft environments. |
| 🛡 Flexera Vulnerability Management Vendor Flexera - Vulnerability Management |
Enterprise-grade vulnerability and patch management solution designed for large organizations, supporting extensive third-party integrations and centralized vulnerability lifecycle management. |
| ⚙ Tenable Vulnerability Assessment Vendor Tenable - Solutions for Vulnerability Assessment |
Enterprise-class vulnerability and patch management platform supporting Microsoft, Linux and macOS environments, helping organizations identify, prioritize and remediate vulnerabilities efficiently. |
Member States shall ensure that essential and important entities establish policies and procedures for assessing, monitoring and improving the effectiveness of their cybersecurity risk-management measures.
| 📊 Sophos Managed Detection & Response (MDR) Vendor Sophos - Managed Detection and Response (MDR) |
Continuously investigates and assesses potential cybersecurity risks across the entire environment using advanced threat intelligence from Sophos X-Ops. Provides ongoing visibility into risk levels, threat exposure and response effectiveness to support continuous improvement of cybersecurity controls. |
Member States shall ensure that essential and important entities implement basic cyber hygiene practices and provide regular cybersecurity training to improve awareness, reduce human-related risks and strengthen overall cyber resilience.
| 🎓 Sophos Training & Certifications Vendor Sophos - Training and Certifications |
Provides professional cybersecurity training courses and certification programs that help IT administrators, security teams and partners strengthen cybersecurity skills, maintain best practices and improve operational security knowledge. |
| 🎣 Sophos Phish Threat Vendor Sophos - Phish Threat |
Provides simulated phishing campaigns and cybersecurity awareness training for end users. Training covers phishing recognition, password security, data loss prevention, social engineering awareness and general cybersecurity best practices to reduce human-related security risks. |
Member States shall ensure that essential and important entities implement policies and procedures regarding the use of cryptography and, where appropriate, encryption to protect information, systems and communications.
| 🔒 Sophos Central Device Encryption Vendor Sophos - Central Device Encryption |
Protects devices and sensitive data through full disk encryption for Windows and macOS systems. Enables organizations to verify encryption status and demonstrate compliance with security policies. |
| ☁ Microsoft Security Stack Microsoft - Technological Stack of Solutions |
Provides protection of devices and corporate data through full disk encryption technologies managed and controlled through Microsoft Cloud services. |
| 💾 Acronis Cyber-Protected Backup Vendor Acronis - Cyberprotected Backup |
Combines backup and cyber protection capabilities to secure business-critical information. Extends cloud backup capabilities with integrated protection mechanisms designed to safeguard data from cyber threats. |
| ✉ Sophos Email Protection Vendor Sophos - Email Solution Brief Vendor Sophos - Next Generation Firewall |
Supports TLS encryption and secure email communications through SMTP/S. Includes optional portal-based encryption capabilities for protecting sensitive communications and information exchange. |
| 📱 Sophos Mobile Vendor Sophos - Mobile |
Enforces mobile device encryption policies and continuously monitors compliance with organizational encryption requirements. |
Member States shall ensure that essential and important entities implement human resources security measures, access control policies and asset management processes to maintain secure access to information and information systems.
| 🚨 Sophos MDR Vendor Sophos - Managed Detection and Response (MDR) |
Monitors and correlates activity across the security environment, identifying suspicious behavior through analysis of audit logs, access logs, security reports and incident-tracking information. |
| 🔥 Sophos Next Generation Firewall Vendor Sophos - Next Generation Firewall |
Provides user-aware security controls, reporting and policy enforcement, enabling granular management of applications, bandwidth usage and network resources based on user identity. |
| 👤 Sophos Central Vendor Sophos - Sophos Central |
Maintains user privileges, access rights and access control records. Supports administrative processes to ensure user access is promptly updated, revoked or modified when employment or responsibilities change. |
| 🔐 Sophos ZTNA Vendor Sophos - Sophos ZTNA |
Improves access control and user lifecycle management by continuously validating user identity, device health and compliance before granting access to applications and corporate resources. |
| ☁ Sophos Cloud Optix Vendor Sophos - Cloud Optix SECaaS |
Provides inventory management across cloud environments with continuous asset monitoring, network topology visibility and cloud resource tracking. |
| 🖥 Acronis Software Inventory Vendor Acronis - Software Inventory |
Provides endpoint monitoring, asset inventory, patch management, scripting automation and centralized visibility of deployed software and managed devices. |
Member States shall ensure that essential and important entities implement multi-factor authentication, continuous authentication solutions, secure communications and secure emergency communication systems where appropriate.
| 🔐 Sophos Next Generation Firewall Vendor Sophos - Next Generation Firewall |
Supports flexible multi-factor authentication capabilities and integration with directory services to secure access to critical systems and infrastructure. |
| 🛡 Sophos ZTNA Vendor Sophos - Sophos ZTNA |
Continuously validates user identity, device posture and compliance status before granting access to applications and corporate resources, supporting zero-trust access principles. |
| 👤 Sophos Central Vendor Sophos - Sophos Central |
Protects privileged and administrative accounts through advanced two-factor authentication mechanisms and centralized identity management controls. |
| ☁ Sophos Cloud Optix Vendor Sophos - Cloud Optix SECaaS |
Monitors AWS, Microsoft Azure and Google Cloud environments for privileged accounts and identifies users with MFA disabled, supporting enforcement of strong authentication requirements and compliance controls. |
Member States shall ensure that essential and important entities submit incidents notifications and final reports to the competent authorities, including a detailed description of the incident, its severity, impact, root cause, threat type and remediation measures undertaken.
| 🚨 Sophos Managed Detection & Response (MDR) Vendor Sophos - Managed Detection and Response (MDR) |
Supports incident reporting requirements through continuous monitoring, investigation and incident response. Upon notification, Sophos MDR performs a full investigation to identify indicators of compromise, determine the impact and severity of the incident, provide remediation actions and deliver a detailed human-authored report suitable for incident documentation and reporting purposes. |
| 📊 Logsign Unified SecOps Platform Vendor Logsign - Unified SecOps Platform Bundle |
Provides SIEM and SOAR capabilities with advanced reporting functions designed for medium and enterprise organizations. Enables incident analysis, event correlation, compliance reporting and investigation workflows required for regulatory reporting obligations. |
| ☁ Logpoint SIEM & SOAR Platform Vendor Logpoint - SIEM & SOAR Solution with UEBA Capabilities |
Provides centralized log management, threat detection, incident investigation, UEBA analytics and comprehensive reporting capabilities. Supports organizations in documenting cybersecurity incidents, identifying impacts and producing reports required for regulatory compliance and audit purposes. |
| 🔍 Sophos Managed Detection & Response (MDR) Vendor Sophos - Managed Detection and Response (MDR) |
Leverages Sophos X-Ops threat intelligence and expert-led investigations to determine likely attack vectors, threat types and root causes of cybersecurity incidents. Provides full root cause analysis, investigation findings and recommendations that help organizations improve resilience and strengthen future incident response processes. |
| 📈 Sophos XDR Vendor Sophos - Sophos XDR |
Aggregates endpoint, network, cloud, email and mobile telemetry into a centralized data lake, enabling security teams to investigate incidents, correlate events, identify attack paths and determine the underlying causes of cybersecurity incidents. |
| 📊 Logsign Unified SecOps Platform Vendor Logsign - Unified SecOps Platform Bundle |
Provides log analytics, correlation rules, security monitoring and investigation capabilities that help identify threat sources, attack patterns and incident root causes while supporting reporting and forensic analysis activities. |
| ☁ Logpoint SIEM & SOAR Platform Vendor Logpoint - SIEM & SOAR Solution with UEBA Capabilities |
Combines SIEM, SOAR and UEBA capabilities to analyze security events, identify anomalous activity, determine root causes and generate detailed reports supporting incident investigations and regulatory reporting requirements. |
NIS2 Compliance Checklist
The NIS2 Directive requires organizations to implement cybersecurity risk-management measures, governance controls, business continuity procedures, incident response capabilities and security monitoring controls.
Governance
✓ Management oversight
✓ Cybersecurity policies
✓ Risk management framework
✓ Security awareness training
Security Controls
✓ MDR / SOC monitoring
✓ Vulnerability management
✓ Endpoint protection
✓ Network security
Incident Management
✓ Incident response plan
✓ Reporting procedures
✓ Threat detection
✓ Root cause analysis
Business Continuity
✓ Backup management
✓ Disaster recovery
✓ Business continuity planning
✓ Crisis management procedures
Access & Data Protection
✓ Multi-factor authentication
✓ Encryption
✓ Access control policies
✓ Asset management
Supply Chain Security
✓ Third-party risk assessments
✓ Supplier security reviews
✓ Vendor access controls
✓ Continuous monitoring
Frequently Asked Questions About NIS2
Find answers to some of the most common questions organizations ask when preparing for NIS2 compliance.
What is the NIS2 Directive?
The NIS2 Directive is the European Union's cybersecurity legislation designed to improve the resilience and security of organizations operating in critical and important sectors. It introduces stronger governance, cybersecurity risk management and incident reporting requirements.
Who must comply with NIS2?
NIS2 applies to Essential Entities and Important Entities operating in sectors such as energy, transport, healthcare, manufacturing, banking, digital infrastructure, public administration, ICT services and many others.
When does NIS2 apply?
The NIS2 Directive became applicable across the European Union on 18 October 2024 following the transposition period provided to EU Member States.
What are the main NIS2 requirements?
Organizations must implement cybersecurity risk management measures covering governance, incident handling, business continuity, disaster recovery, vulnerability management, supply chain security, employee awareness training, encryption, multi-factor authentication and reporting obligations.
What happens if an organization is not compliant?
Organizations may face regulatory investigations, corrective measures, reputational damage and financial penalties depending on national legislation and the severity of non-compliance.
What are Essential and Important Entities?
NIS2 classifies covered organizations as either Essential Entities or Important Entities based on factors such as sector, size and importance to society and the economy.
How long does it take to become NIS2 compliant?
The timeframe varies depending on your current cybersecurity maturity. Organizations with existing governance, monitoring and security controls may require only a gap assessment and remediation plan, while others may need a broader compliance program.
How can AdvisionIT help with NIS2 compliance?
AdvisionIT provides cybersecurity consulting, MDR, XDR, SIEM, security awareness training, vulnerability management, incident response, business continuity solutions and NIS2 readiness assessments to help organizations achieve and maintain compliance.

How Can Advanced Vision IT Help You Comply with the NIS2 Directive?
Achieving NIS2 compliance requires the right combination of people, processes and technology. Advanced Vision IT helps organizations identify compliance gaps, implement cybersecurity controls, strengthen resilience and build a practical roadmap toward NIS2 readiness.
Governance & Risk Management
✓ NIS2 Readiness Assessments
✓ Compliance Gap Analysis
✓ Governance Frameworks
✓ Risk Management Programs
Managed Security Services
✓ MDR & XDR Services
✓ SIEM & SOC Solutions
✓ Incident Response
✓ Continuous Monitoring
Cyber Resilience
✓ Vulnerability Management
✓ Security Awareness Training
✓ Backup & Disaster Recovery
✓ Business Continuity
Need Help Understanding Your NIS2 Obligations?
Book a free consultation and let's discuss your organization, identify potential compliance gaps, and determine the most practical path toward NIS2 compliance.
📅 Book a Call with Me
ADVANCED VISION IT - MALTA
Address: Suite 8, Ta’ Mallia Buildings, Triq In‑Negozju, Zone 3, Central Business District, Birkirkara, CBD 3010, Malta
Registration number: C111282, VAT Number: MT31713827
Phone:+35679224404
Email: office@advisionit.com
ADVANCED VISION IT - BULGARIA
Advanced Vision IT LTD
Address: District Triaditsa, Tulcha Street No. 46, Floor 6, Sofia, Bulgaria
ID No: 205789039,
VAT No: BG205789039
Phone: +359 888258530
Email: office@advisionit.com